How to Prevent an Intune Bulk Wipe: Sentinel KQL + Hardening
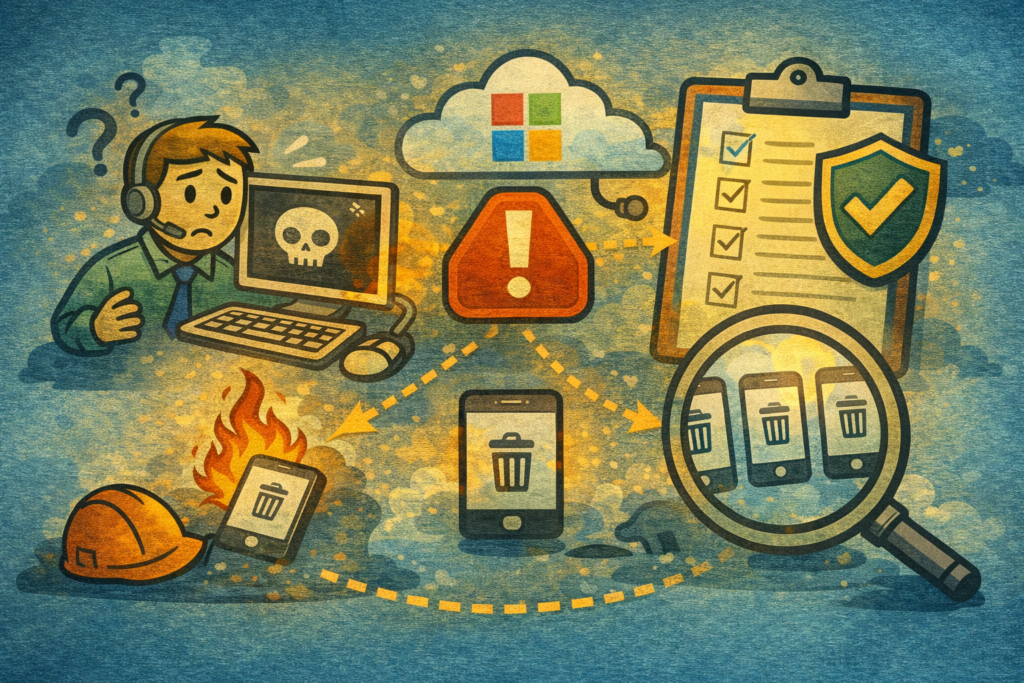
This week a global medical technology company had their Microsoft tenant compromised. The attackers didn’t deploy custom malware. They logged into the Intune admin console and used the built-in device management tools to trigger a bulk wipe across the entire managed device fleet. From the field: This is the detection rule I would want in
How to Prevent an Intune Bulk Wipe: Sentinel KQL + Hardening Read More »